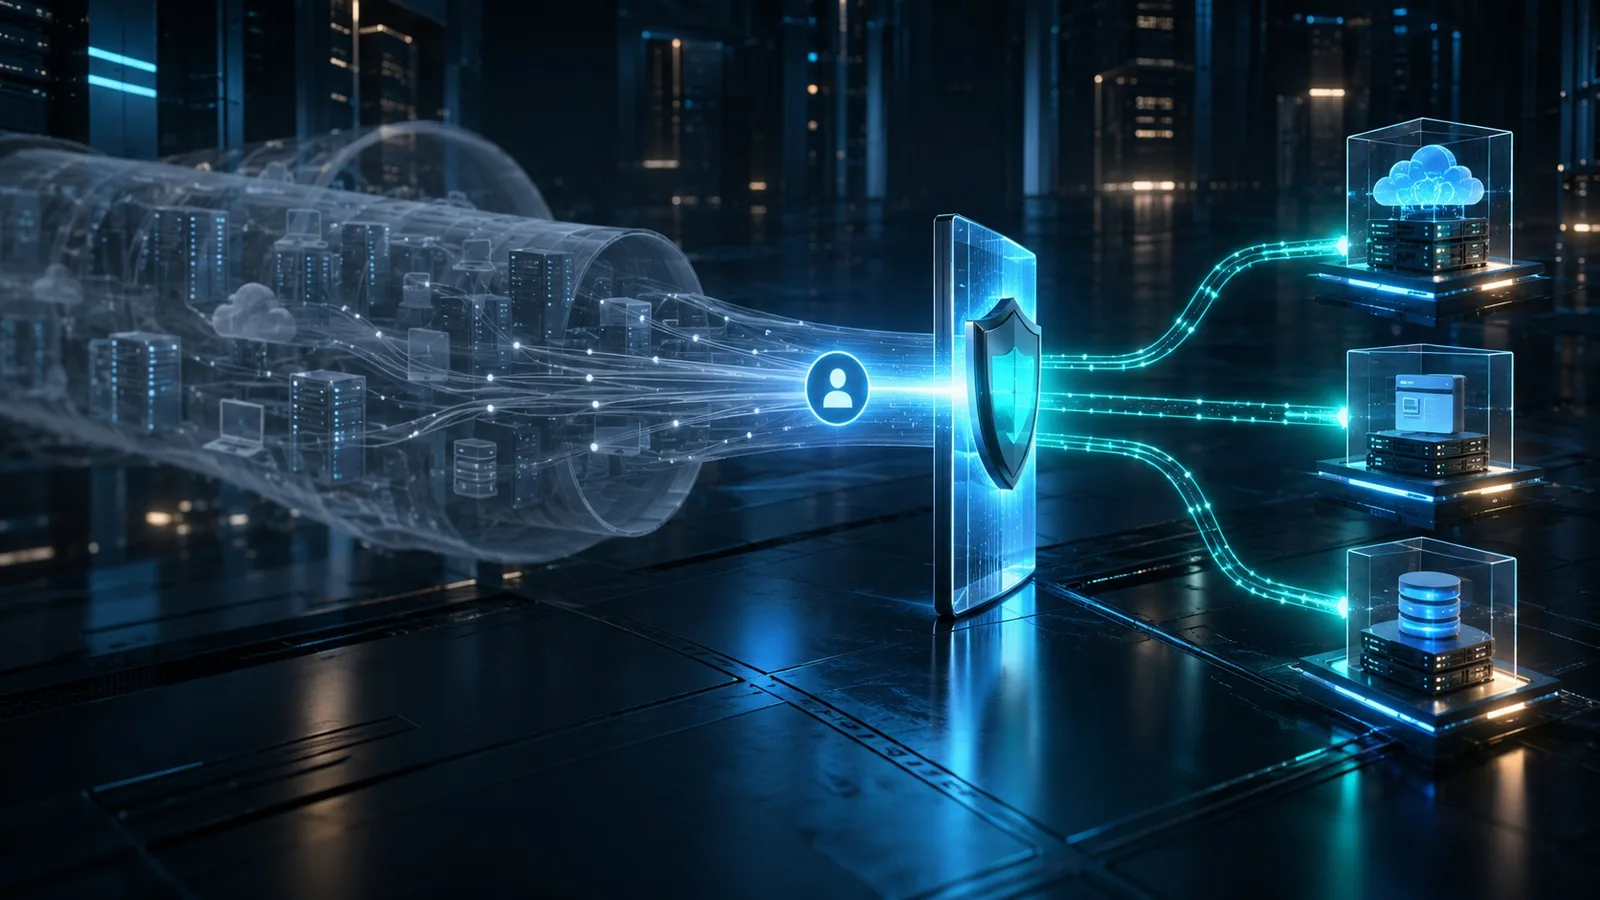
For years, remote access was provided through an encrypted tunnel into the enterprise network. This model first places the user on the network and then allows access to resources within it. As cloud services, distributed teams, and devices with different levels of management have increased, broad network access has become harder to control. If an account or device is compromised, an attacker may have more room to perform discovery inside the network.
Zero trust network access, or ZTNA, aims to give a user access only to an authorized application or resource instead of a broad network segment. The decision evaluates identity, device condition, the requested resource, session risk, and access conditions together. The purpose of the transition is not merely to replace the remote-access tool. It is to move access policy from network location to application and identity context.
The fundamental difference between VPN and ZTNA
A virtual private network connection creates an encrypted channel between a user’s device and the enterprise network. Authorization takes place at the gateway. After the connection is established, routing, network segments, and firewall rules often limit the scope of access. This design can be secure when implemented properly, but the authorization relationship between a user and an application may be difficult to see clearly.
Depending on the architecture, ZTNA solutions provide access to specific enterprise resources through a gateway, connector, or broker layer. Hiding the application from the public network is common, although not universal. Authentication and authorization take place before a session to the enterprise resource is established and can be reevaluated during the session when policy requires it. The user is not routed to the entire network that hosts the application. NIST SP 800-207 states that network location or device ownership alone should not be treated as a basis for trust in this approach.
This difference does not mean that the VPN must be removed immediately. Network administration, certain legacy protocols, and limited tasks that require access to an entire subnet rather than a single application may continue to use a VPN for some time. The migration plan should distinguish workloads suited to application-level access and narrow the network access that remains.
Resource inventory and access mapping
A ZTNA project begins with a resource inventory, not a product installation. List internet-facing applications, web applications in the data center, remote desktop services, management interfaces, and legacy systems that use proprietary protocols separately. For each resource, record the service owner, data class, identity method, dependencies, user groups, and expected access path.
Existing VPN logs provide important evidence about real usage. They can show which groups connect to which destinations, at what times, and how often. Network flows alone are not enough. Supporting services opened within a session, domain-name resolution, certificate validation, and identity-provider connections must also be mapped. Otherwise, the main application may open during the pilot while a critical dependency fails.
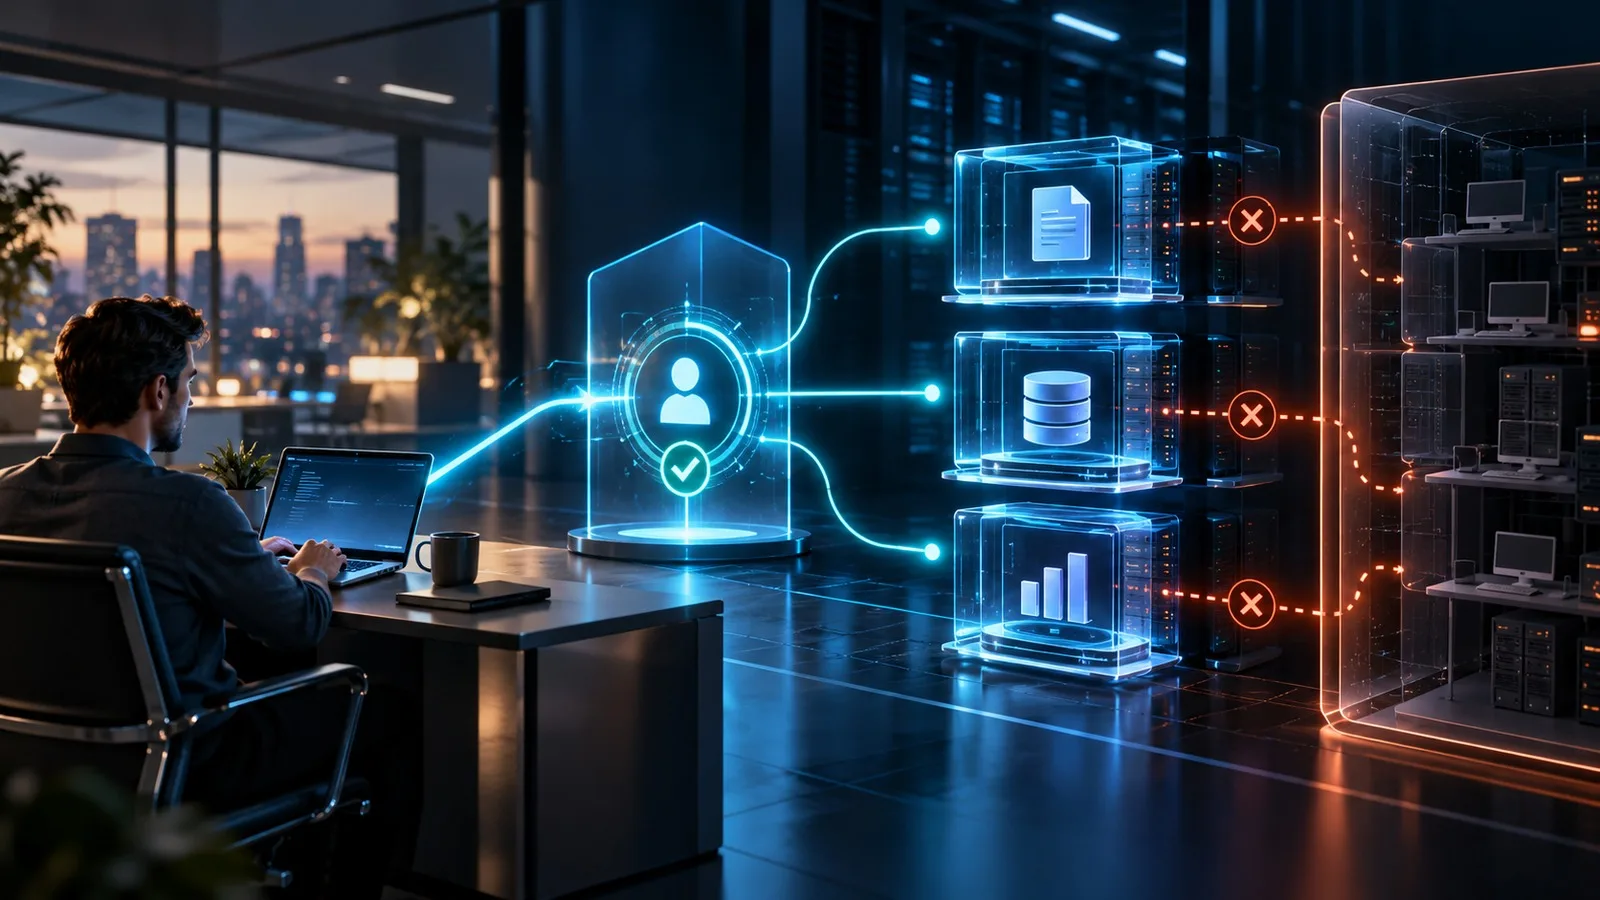
Once the inventory is complete, classify applications by migration difficulty and risk. Applications that use standard web protocols, depend on centralized authentication, and have a known owner are suitable for the first pilot. Administrative tools that scan networks, systems that use many dynamic ports, and legacy applications without identity integration require more detailed design.
Identity, device, and context signals
The reliability of application-level access depends on accurate identity and device information. Individual accounts, strong multifactor authentication, and timely removal of access rights are baseline requirements. Shared accounts, permanent administrative privileges, and long-lived sessions weaken access decisions. Sensitive actions may require reauthentication or a stronger verification step.
Device condition should not be reduced to one compliance label. Evaluate a supported operating system, security updates, disk encryption, screen lock, endpoint protection, and device enrollment as separate signals. If access from a personal device is allowed, actions such as downloading, copying, or printing application data may require distinct rules.
Context signals are useful, but they should not determine the outcome on their own. Access from an unusual country, an anonymizing network, distant locations within a short period, or unexpected hours may raise the risk score. Because false positives can interrupt work, responses to high risk should be defined in advance. Options can include blocking access, requiring additional verification, allowing read-only access, or shortening the session.
Policy decision and enforcement layers
In a ZTNA architecture, the policy decision point gathers signals about the access request and produces an authorization decision. The policy enforcement point opens, limits, or denies the connection. When these roles are logically separated, access rules can be managed centrally and different application gateways can apply the same policy approach.
Policies should not grow into direct lists of individuals. Use attributes such as role, task, resource sensitivity, device level, and access purpose. A managed device and strong authentication may be sufficient for a standard application, while an administrative interface may require a privileged role, a controlled device, and an approved time window. Every rule should have an owner, justification, review date, and defined failure behavior.
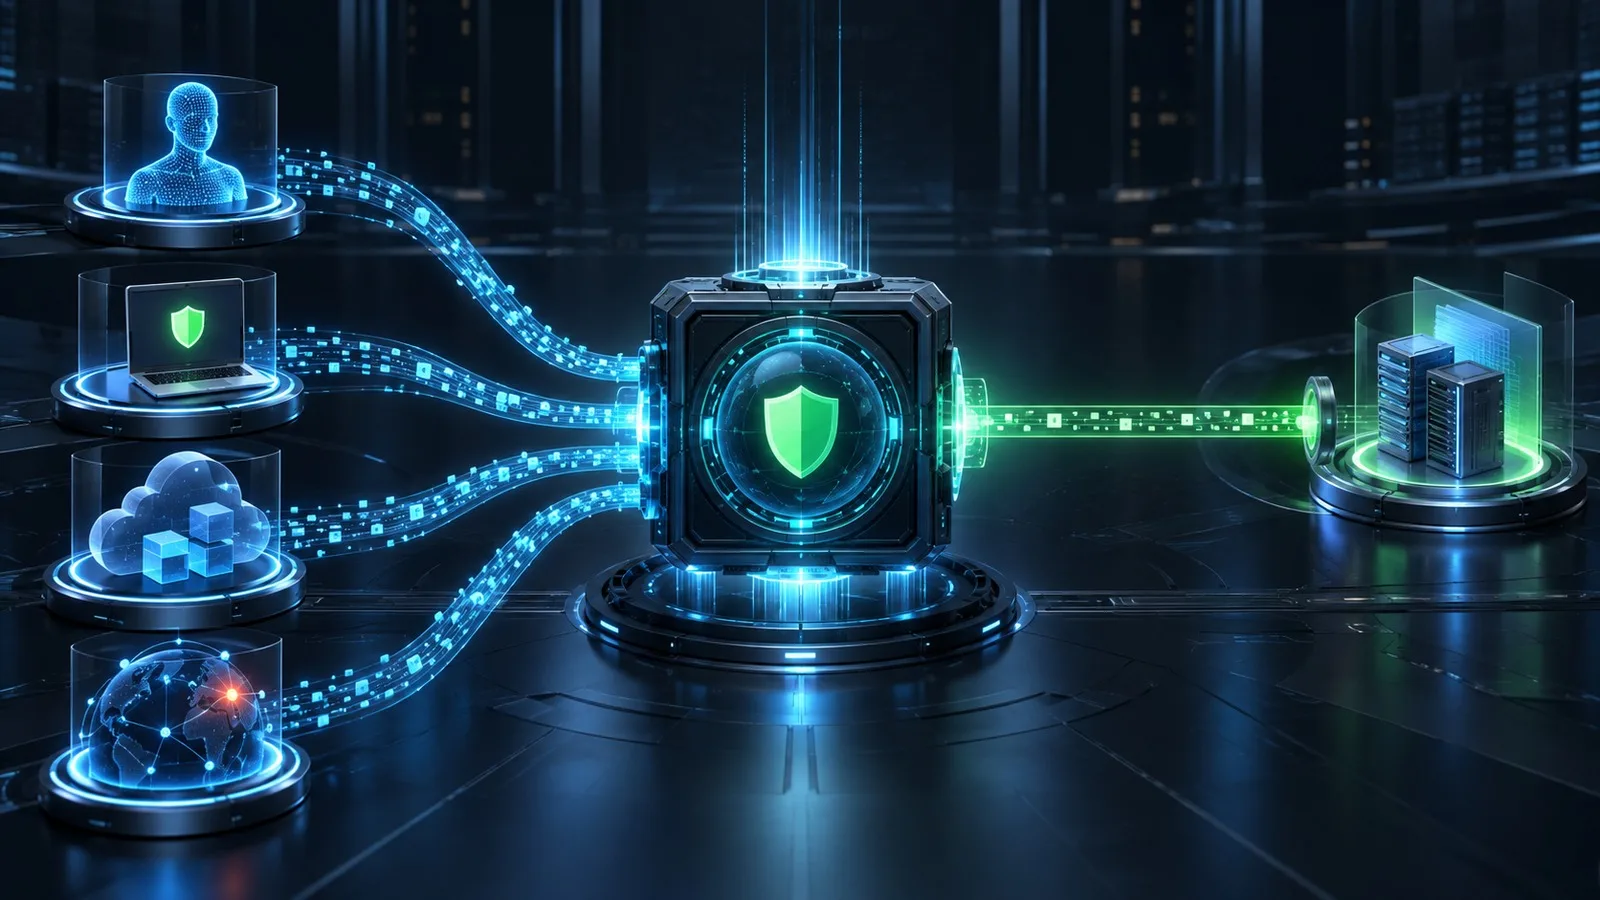
An application connector or access gateway can be placed so that it initiates an outbound connection to the protected resource. The application then does not need to be exposed directly to the internet. Even so, the gateways themselves are critical infrastructure and require high availability, patching, certificate management, and logging.
Migration sequence and coexistence period
The first pilot should use a small but representative user group and two or three applications with limited impact. Success means more than establishing a connection. Measure sign-in time, application response, reasons for denied access, support needs, and the recovery path during an outage. The new access path and the existing VPN can run in parallel during the pilot, but the conditions for using each path should be clear so that users do not continually return to the old route.
In later waves, applications can be grouped by business unit, protocol, and risk level. Before each wave, verify dependencies, clean up access groups, and adjust policy using the pilot results. If VPN scope does not shrink at the same pace, two separate access layers will become permanent. When an application moves to ZTNA, close its old network path or restrict it to an emergency account.
Administrative access requires a separate migration track. Teams that manage servers, network devices, or databases may need recorded sessions, time-limited authorization, command-level controls, and emergency access. Combining standard user access and administrator access in one policy set reduces visibility.
Performance, continuity, and incident response
A ZTNA service depends on several components, including the identity provider, name resolution, certificate infrastructure, and application gateways. The design should explain what happens when one of these dependencies fails. Test in advance how long existing sessions remain active, whether new sessions can be opened, and how emergency access is verified during an identity-service outage.
Monitor the user experience end to end. Gateway latency, user location, the internet path, authentication time, and the application’s own response should appear on the same timeline. An architecture that sends traffic to an unnecessarily distant point may slow the application even while improving security. Select gateway locations and connection routes using real-user measurements.
For incident response, link the application, user, device, and policy decision through one session identifier. When suspicious access appears, the team should be able to terminate the affected session, quarantine the device, and examine other sessions opened with the same identity instead of only disabling the account. Define log-retention periods and access rights together with privacy and regulatory requirements.
Common mistakes
The most common mistake is copying existing VPN rules directly into the new platform. Moving broad subnet permissions into an application-level model does not reduce the access surface. The second is applying the same device and risk policy to every user. Control levels should differ when application sensitivity and job functions differ.
Other mistakes include excluding the application owner from the process, tracking only the number of successful sessions, leaving legacy access paths open, managing service accounts like human accounts, and failing to test an emergency scenario. ZTNA also does not remove malware from an endpoint or fix a vulnerability in the application. Endpoint security, secure software development, network segmentation, and log management must continue alongside it.
A phased implementation plan
In the first phase, create an application and access inventory, validate VPN flows, and establish baseline measurements. In the second, integrate identity, device, and log sources. In the third, run a pilot with low-risk web applications and review support records and the user experience.
In the fourth phase, apply step-up authentication, short sessions, and time-limited authorization to more sensitive applications. In the fifth, close the old network paths for migrated applications, document the justification for remaining VPN use, and begin regular entitlement reviews. In the final phase, update access policies using incident data and changing business requirements.
Implementation checklist
· Are the owner, data class, and dependencies of protected applications recorded?
· Does every user group have access only to the applications required for its work?
· Is the freshness of identity and device signals verified?
· Has the old VPN path been closed for applications moved to ZTNA?
· Is there a tested plan for gateway, identity, and name-resolution outages?
· Can session logs be correlated with the application, user, device, and policy decision?
Sources
· NIST SP 800-207 Zero Trust Architecture (https://csrc.nist.gov/pubs/sp/800/207/final)
· NIST SP 800-207A Zero Trust Access Control for Cloud Native Applications (https://csrc.nist.gov/pubs/sp/800/207/a/final)
· NIST CSWP 20 Planning for a Zero Trust Architecture (https://csrc.nist.gov/pubs/cswp/20/planning-for-a-zero-trust-architecture/final)
· CISA Zero Trust Maturity Model Version 2 (https://www.cisa.gov/sites/default/files/2023-04/zero_trust_maturity_model_v2_508.pdf)
· NIST SP 1800-35 Implementing a Zero Trust Architecture (https://csrc.nist.gov/pubs/sp/1800/35/final)
· NIST SP 800-46 Rev 2 Enterprise Telework and Remote Access Security (https://csrc.nist.gov/pubs/sp/800/46/r2/final)